
Binance Suffers $6.3 Billion Crypto Theft Attributed to North Korean Group TraderTraitor
Why it matters
The compromise of centralized automated signing infrastructure demonstrates that human-layer access vectors can bypass on-chain protections at a sovereign-scale financial level.
What happened (in 30 seconds)
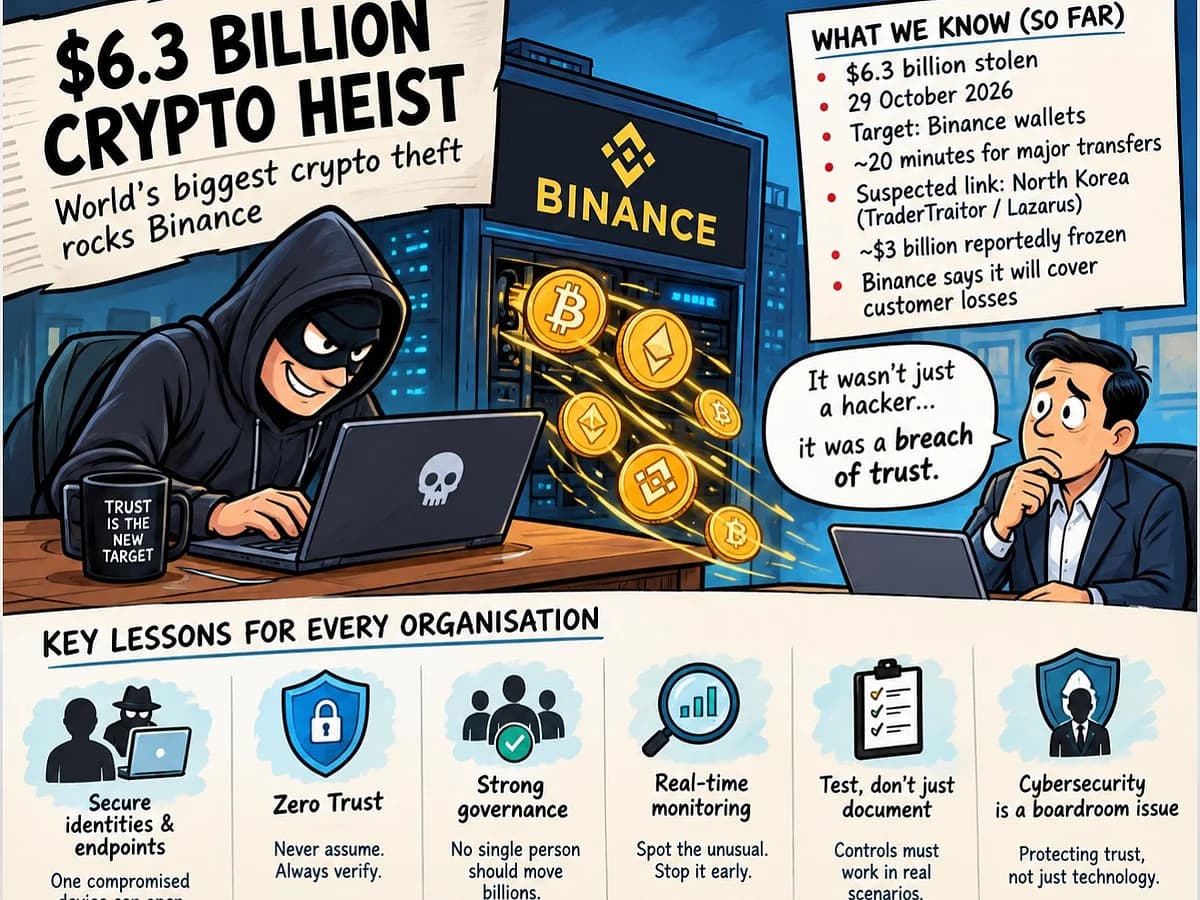
- Rapid balance drainage: Between October 29 and 30, 2026, attackers compromised Binance’s signing infrastructure, moving roughly $6.3 billion across multiple blockchains in approximately 20 to 30 minutes.
- Endpoint origin vector: Initial unauthorized entry occurred via a compromised DevOps engineer's laptop, granting the attackers operational access to approve automated hot-wallet outflows.
- Mitigation and recovery: Stablecoin issuers Tether and Circle froze approximately half of the outbound volume within hours, while Binance halted withdrawals and activated its Secure Asset Fund for Users (SAFU) alongside corporate reserves to backstop client balances.
The context you actually need
- State-sponsored operational record: The Federal Bureau of Investigation formally attributed the operation to TraderTraitor, a North Korean state-linked cyber syndicate that previously executed the $1.5 billion Bybit theft in 2025.
- Infrastructure attack surfaces: Digital asset platforms handling billions in daily transactions have relied heavily on hot wallets and automated signing workflows to minimize withdrawal latency for global users.
- The baseline disparity: While decentralized ledger mechanics functioned as intended, internal role-based trust controls allowed an adversary to extract more than four times the value lost in any prior digital asset theft.
What's really happening
The Binance intrusion exposes the fundamental friction between processing velocity and asset security in centralized exchange architectures. For platforms serving tens of millions of active accounts, competitive positioning demands near-instantaneous liquidity routing. To fulfill market demand for sub-second execution, centralized exchanges depend on automated signing servers connected directly to online hot wallets.
The structural failure in this instance was not a cryptographic breakdown of distributed ledger technology. Instead, it was an operational identity breakdown. By compromising a single endpoint—a DevOps engineer's laptop—the threat actors inherited authenticated administrative entitlements. This access allowed them to issue valid cryptographic authorizations directly to the transaction-signing pipeline. Once authenticated within the operational perimeter, the attackers bypassed customary multi-party approval safeguards, initiating sequential programmatic withdrawals across multiple networks without triggering automated circuit breakers until 20 to 30 minutes had passed.
This vulnerability profile is shaped by clear structural incentives. Highly competitive trading venues design operational rails to reduce transaction friction and customer support backlogs, which systematically disincentivizes manual verification gates. Conversely, the threat group TraderTraitor operates under state-directed pressure to acquire hard currency reserves in the face of ongoing global sanctions, directing prolonged surveillance toward the few technical personnel who maintain broad infrastructure privileges.
Furthermore, the post-incident containment pattern reveals the growing systemic reliance on centralized intermediaries within permissionless finance. Approximately 50 percent of the diverted capital was contained not through exchange-level interventions, but because centralized stablecoin operators deployed blacklist functions directly on secondary market smart contracts. While this intervention insulated Binance's immediate balance sheet exposure, it establishes a distinct precedent: systemic liquidity preservation increasingly depends on the manual discretion of fiat-backed stablecoin issuers during catastrophic security events.
Who feels it first (and how)
- Digital asset treasurers and institutional allocators: Corporate treasury teams managing exposure on centralized platforms face direct operational halts during emergency withdrawal freezes, forcing re-evaluations of third-party custodial counterparties.
- Fintech infrastructure engineers and CISOs: Security personnel across exchanges and non-bank payment rails face immediate mandates to implement behavioral anomaly detection and dismantle persistent access privileges on administrative devices.
- Regional operators in the UAE: As a major hub for digital asset volume, Dubai-based financial entities and market participants face intensified local supervisory compliance audits, rigorous zero-trust requirements, and operational latency following regional exposure to the 2025 Bybit incident and this breach.
- Retail token holders: General depositors experience indirect pricing drag from liquidity crunches and localized price depreciation across primary assets such as Bitcoin and Ethereum during active security incidents.
What to watch next
- Implementation of multi-party authorization protocols: Watch for whether major trading platforms deploy multi-party computation models that require distributed, out-of-band quorum approvals for programmatic withdrawals, which will indicate a structural departure from single-engineer signing access.
- Stablecoin address blacklist resolutions: Track the legal and operational mechanisms used to process and reassign the frozen $3.1 billion in stablecoin assets, as this reveals how centralized asset issuers interact with judicial recovery proceedings.
- Regional exchange audit timelines: Monitor regulatory reporting periods across key virtual asset jurisdictions like Dubai, where domestic supervisory authorities are positioned to enforce mandatory zero-trust verification frameworks on registered platforms.
TraderTraitor executed the extraction of $6.3 billion from Binance hot wallets over a 20-to-30-minute span starting after 20:00 GMT on October 29, 2026, through a compromised DevOps endpoint. Stablecoin issuers froze roughly half of the funds, and Binance deployed its SAFU reserve and corporate capital to cover client shortfalls.
Centralized exchanges will intentionally increase withdrawal processing times on non-standard volumes to introduce automated behavioral monitoring delays, elevating transaction friction for institutional accounts.
The exact proportion of un-frozen assets that can be recovered before laundering through decentralized obfuscation layers remains uncertain, as does the long-term solvency impact on exchange insurance reserves if secondary attacks occur.
Frequently Asked Questions
- Why it matters?
- The compromise of centralized automated signing infrastructure demonstrates that human-layer access vectors can bypass on-chain protections at a sovereign-scale financial level.
- What happened (in 30 seconds)?
- Rapid balance drainage: Between October 29 and 30, 2026, attackers compromised Binance’s signing infrastructure, moving roughly $6.3 billion across multiple blockchains in approximately 20 to 30 minutes. Endpoint origin vector: Initial unauthorized entry occurred via a compromised DevOps engineer's laptop, granting the attackers operational access to approve automated hot-wallet outflows. Mitigation and recovery: Stablecoin issuers Tether and Circle froze approximately half of the outbound volum
- What's really happening?
- The Binance intrusion exposes the fundamental friction between processing velocity and asset security in centralized exchange architectures. For platforms serving tens of millions of active accounts, competitive positioning demands near-instantaneous liquidity routing. To fulfill market demand for sub-second execution, centralized exchanges depend on automated signing servers connected directly to online hot wallets. The structural failure in this instance was not a cryptographic breakdown of
- Who feels it first (and how)?
- Digital asset treasurers and institutional allocators: Corporate treasury teams managing exposure on centralized platforms face direct operational halts during emergency withdrawal freezes, forcing re-evaluations of third-party custodial counterparties. Fintech infrastructure engineers and CISOs: Security personnel across exchanges and non-bank payment rails face immediate mandates to implement behavioral anomaly detection and dismantle persistent access privileges on administrative devices. Reg
- What to watch next?
- Implementation of multi-party authorization protocols: Watch for whether major trading platforms deploy multi-party computation models that require distributed, out-of-band quorum approvals for programmatic withdrawals, which will indicate a structural departure from single-engineer signing access. Stablecoin address blacklist resolutions: Track the legal and operational mechanisms used to process and reassign the frozen $3.1 billion in stablecoin assets, as this reveals how centralized asset is
24/7 international news from a French perspective in multiple languages.
"France 24 is viewed as a globally focused outlet with balanced coverage and a European perspective."
— A47 Editor
Binance hit by 6.3 billion dollar crypto theft
Binance, the world's largest cryptocurrency exchange, has been hit by a security breach affecting an estimated $6.3 billion in assets, which would make it the largest crypto heist on record. The exchange halted withdrawals and said roughly $3 billion...
A curated Gulf News feed featuring major stories across news, business, opinion, and lifestyle.
"Gulf News is a major UAE newspaper whose featured stories feed reflects a broad editorial mix shaped for a Gulf audience."
— A47 Editor
$6.3b crypto heist: When trust becomes the biggest cybersecurity vulnerability
Binance, the world's largest cryptocurrency exchange, reported a security breach estimated at $6.3 billion in affected assets, described as potentially the largest crypto theft on record. The exchange froze deposits and withdrawals while it investiga...
UAE-based newspaper covering Gulf politics, society, and international developments.
"Gulf News is one of the UAE’s most prominent English-language publications."
— A47 Editor
$6.3b crypto heist: When trust becomes the biggest cybersecurity vulnerability
Binance, the world's largest cryptocurrency exchange, reported a security breach estimated at $6.3 billion in affected assets, described as potentially the largest crypto theft on record. The exchange froze deposits and withdrawals while it investiga...
24/7 international news from a French perspective in multiple languages.
"France 24 is viewed as a globally focused outlet with balanced coverage and a European perspective."
— A47 Editor
Biggest hack in history: Cryptocurrency giant Binance loses $6.3 billion
Binance, the world's largest cryptocurrency exchange, has been hit by a security breach affecting an estimated $6.3 billion in assets, which would make it the largest crypto heist on record. The exchange said roughly $3 billion of the stolen funds ha...
24/7 international news from a French perspective in multiple languages.
"France 24 is viewed as a globally focused outlet with balanced coverage and a European perspective."
— A47 Editor
How the record-breaking $6.3 billion heist in crypto history unfolded
Binance, the world's largest cryptocurrency exchange, was hit by a security breach affecting an estimated $6.3 billion in assets, which would make it the largest crypto heist on record. Issuers have frozen roughly half of the stolen funds, with about...
Culture, society, and public-interest stories for Arabic-speaking readers.
"This Al Watan feed appears section-specific, and the label is kept broad enough to avoid overclaiming the exact mapping."
— A47 Editor
اختراق يهدد 6.3 مليارات دولار بالعملات الرقمية
Binance, the world's largest cryptocurrency exchange, was hit by a security breach that it estimates affected about $6.3 billion in assets, potentially the largest crypto theft on record. The exchange froze deposits and withdrawals while investigatin...
UAE-based English-language newspaper covering regional politics, economics, and global affairs.
"The National reflects Emirati policy perspectives while maintaining international editorial standards."
— A47 Editor
How a $6 billion hack became the world's biggest crypto theft
The National reports that a hack of roughly $6 billion has become the largest cryptocurrency theft on record, according to the base article published on October 30, 2026, which is categorized under Middle East coverage and carries a negative sentimen...
A curated Gulf News feed featuring major stories across news, business, opinion, and lifestyle.
"Gulf News is a major UAE newspaper whose featured stories feed reflects a broad editorial mix shaped for a Gulf audience."
— A47 Editor
Binance reports $6.3 billion security breach, freezes $3 billion in crypto
Binance, the world's largest cryptocurrency exchange, said it was hit by a security breach estimated at $6.3 billion in affected assets, potentially the largest crypto theft on record. The exchange froze deposits and withdrawals while investigating a...
UAE-based newspaper covering Gulf politics, society, and international developments.
"Gulf News is one of the UAE’s most prominent English-language publications."
— A47 Editor
Binance reports $6.3 billion security breach, freezes $3 billion in crypto
Binance, the world's largest cryptocurrency exchange, said it was hit by a security breach estimated at $6.3 billion in affected assets, potentially the largest crypto theft on record. The exchange froze deposits and withdrawals while investigating a...