
FomoPeek iOS App Poisoning Exposes Security Flaws in Cryptocurrency Applications
If you use cryptocurrency apps, this incident underscores the importance of scrutinizing app security, even in official stores.
Why it matters
The FomoPeek incident reveals vulnerabilities in the app distribution ecosystem, raising alarms about the security of cryptocurrency applications.
What happened (in 30 seconds)
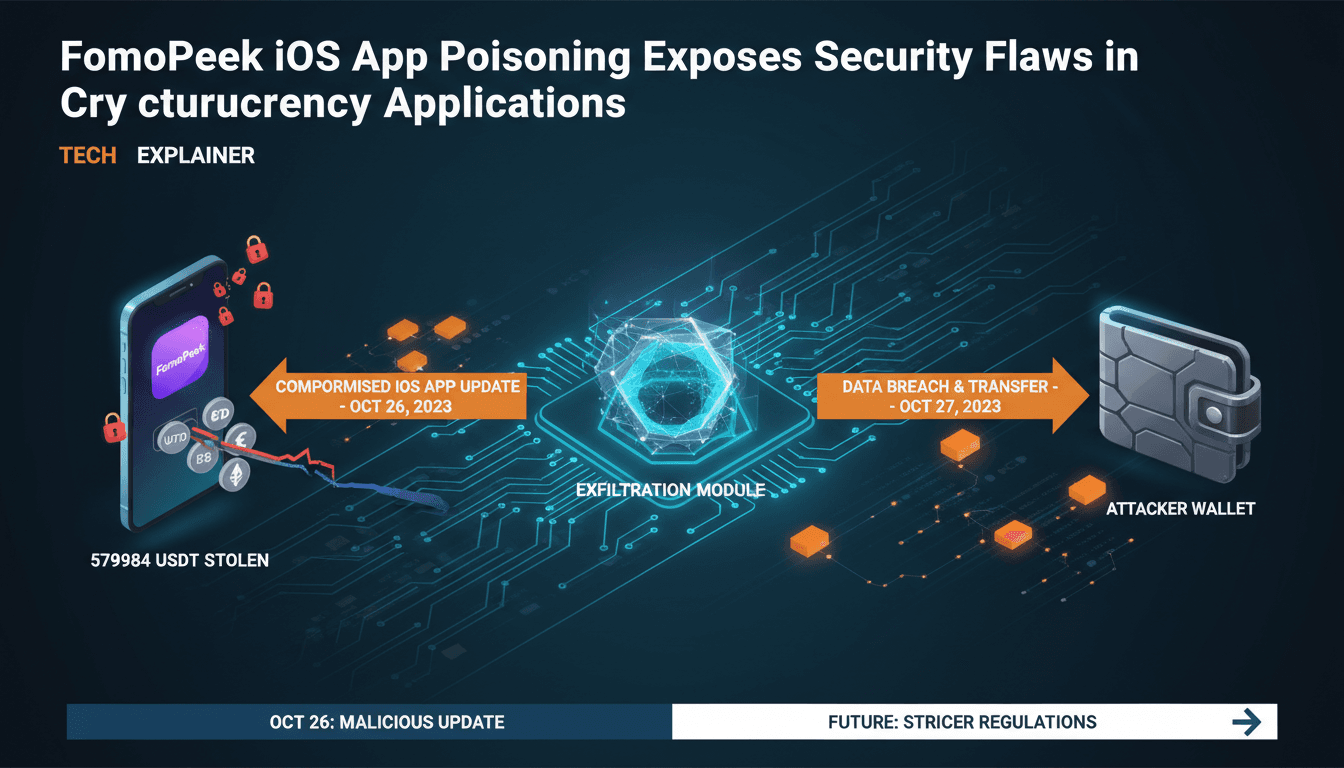
- Malicious code was found in the FomoPeek iOS app, allowing data exfiltration and potential wallet theft.
- 579,984.34 USDT was traced to an attacker wallet linked to the compromised app versions released in September 2026.
- Version 1.3 of the app was released to remove the malicious modules, but users were advised to treat their devices as compromised.
The context you actually need
- Previous incidents: Earlier in 2026, the DarkSword exploit chain demonstrated similar vulnerabilities, allowing zero-click access to wallet data.
- Counterfeit apps: Multiple counterfeit wallet apps had already raised concerns about the security of third-party crypto tools on the App Store.
- Increased scrutiny: The FomoPeek incident has prompted heightened scrutiny of iOS crypto applications, with security firms like SlowMist and OKX advising users to take immediate action.
What's really happening
The FomoPeek iOS app poisoning incident is a stark reminder of the risks associated with supply-chain compromises in the software distribution ecosystem. The app, designed for cryptocurrency monitoring, was found to contain malicious modules that enabled remote command execution and data collection from other applications, including sensitive wallet information. This was particularly alarming given that the app was distributed through Apple's official App Store, a platform typically perceived as secure.
The malicious modules were signed under the same Apple developer identity, which allowed them to bypass standard security checks. This incident highlights a critical vulnerability: even trusted platforms can harbor malicious software, especially in the rapidly evolving cryptocurrency landscape. The attacker wallet, which received 579,984.34 USDT, was activated shortly after the app's release, indicating a well-planned operation aimed at exploiting unsuspecting users.
The implications of this incident extend beyond the immediate financial loss. It raises questions about the effectiveness of current security measures in app distribution channels and the need for more robust vetting processes. As cryptocurrency adoption grows, so does the target market for cybercriminals. Users must remain vigilant, as the potential for similar attacks increases with the proliferation of crypto-related applications.
Moreover, the response from security firms and exchanges, such as Binance's warnings and the advisories from SlowMist and OKX, reflects a growing awareness of these risks. Users are being urged to take proactive measures, such as migrating assets to secure devices and regenerating wallets, to mitigate potential losses. This incident serves as a wake-up call for both users and developers to prioritize security in the development and use of cryptocurrency applications.
Who feels it first (and how)
- Crypto investors: Users of the FomoPeek app who may have had their wallet credentials compromised.
- App developers: Those creating cryptocurrency-related applications must now navigate increased scrutiny and security expectations.
- Security firms: Companies like SlowMist and OKX are likely to see a rise in demand for their services as users seek to protect their assets.
What to watch next
- Increased security measures: Watch for new protocols and vetting processes introduced by app stores to enhance security for cryptocurrency applications.
- User behavior changes: Monitor how users adapt their security practices in response to this incident, such as adopting hardware wallets or multi-factor authentication.
- Regulatory responses: Keep an eye on potential regulatory actions aimed at improving the security of cryptocurrency applications and protecting consumers.
Malicious modules were present in FomoPeek versions 1.1 and 1.2, leading to data exfiltration.
Users will become more cautious about downloading cryptocurrency apps from official stores.
The long-term impact on the cryptocurrency market and user trust in app security remains to be seen.
Frequently Asked Questions
- Why it matters?
- The FomoPeek incident reveals vulnerabilities in the app distribution ecosystem, raising alarms about the security of cryptocurrency applications.
- What happened (in 30 seconds)?
- Malicious code was found in the FomoPeek iOS app, allowing data exfiltration and potential wallet theft. 579,984.34 USDT was traced to an attacker wallet linked to the compromised app versions released in September 2026. Version 1.3 of the app was released to remove the malicious modules, but users were advised to treat their devices as compromised.
- What's really happening?
- The FomoPeek iOS app poisoning incident is a stark reminder of the risks associated with supply-chain compromises in the software distribution ecosystem. The app, designed for cryptocurrency monitoring, was found to contain malicious modules that enabled remote command execution and data collection from other applications, including sensitive wallet information. This was particularly alarming given that the app was distributed through Apple's official App Store, a platform typically perceived as
- Who feels it first (and how)?
- Crypto investors: Users of the FomoPeek app who may have had their wallet credentials compromised. App developers: Those creating cryptocurrency-related applications must now navigate increased scrutiny and security expectations. Security firms: Companies like SlowMist and OKX are likely to see a rise in demand for their services as users seek to protect their assets.
- What to watch next?
- Increased security measures: Watch for new protocols and vetting processes introduced by app stores to enhance security for cryptocurrency applications. User behavior changes: Monitor how users adapt their security practices in response to this incident, such as adopting hardware wallets or multi-factor authentication. Regulatory responses: Keep an eye on potential regulatory actions aimed at improving the security of cryptocurrency applications and protecting consumers.
Covers Bitcoin plus altcoin news, market updates, and educational resources.
"Bitcoin.com provides news, market data, and guides focused on Bitcoin and the wider crypto industry."
— A47 Editor
iPhone Crypto App Hides Malicious Code as Attacker Wallet Nets $580K
A malicious iPhone application named FomoPeek has been linked to the theft of approximately $580,000 in cryptocurrency, exploiting vulnerabilities in Apple's iOS to bypass security measures. The app was distributed through the App Store and has raise...
Covers blockchain, cryptocurrency news, project analysis, and market insights.
"Cointelegraph is a leading crypto-focused media outlet known for timely news, analysis, and educational content related to blockchain and digital assets."
— A47 Editor
Malicious iOS app FomoPeek linked to $580K crypto theft, SlowMist says
A malicious iOS application named FomoPeek has been linked to a theft of approximately $580,000 in cryptocurrency, according to security firm SlowMist. The app, distributed through Apple's App Store, exploited iOS kernel vulnerabilities to bypass sec...
Real-time updates, analysis, and reports on the blockchain and cryptocurrency sectors.
"Crypto News delivers real-time updates, analysis, and reports on the blockchain and cryptocurrency sectors."
— A47 Editor
SlowMist warns Darksword may target wallets on iOS 26.5
SlowMist has issued a warning that the Darksword exploit chain may now target iOS 26.5 devices, potentially compromising self-custody crypto wallets and allowing attackers to extract private keys. This adaptation of the exploit raises significant con...
Covers Bitcoin plus altcoin news, market updates, and educational resources.
"Bitcoin.com provides news, market data, and guides focused on Bitcoin and the wider crypto industry."
— A47 Editor
Slowmist Warns Darksword iOS Exploit Targets Crypto Wallet Keys
Slowmist has issued a warning regarding a new exploit known as Darksword, which targets iOS devices to compromise cryptocurrency wallet keys. This vulnerability poses a significant risk to users' digital assets, as it can lead to unauthorized access ...
Real-time updates, analysis, and reports on the blockchain and cryptocurrency sectors.
"Crypto News delivers real-time updates, analysis, and reports on the blockchain and cryptocurrency sectors."
— A47 Editor
Binance warns iPhone users of FomoPeek malware targeting crypto wallets
Binance has issued a warning to iPhone and iPad users regarding the FomoPeek malware, which has been linked to malicious code that can compromise private keys and seed phrases stored in crypto wallets. Users are advised to check for the installation ...