
Critical Java4Shell Flaw CVE-2026-114938 Enables Unauthenticated Remote Code Execution Across Enterprise Java Systems
What happened
Cybersecurity firm Calif uncovered a critical memory-corruption vulnerability in OpenJDK's Base64 decoder that allows unauthenticated attackers to execute remote code across enterprise Java environments.
The Context
- Infrastructure ubiquity: The flaw (CVE-2026-114938) directly compromises core enterprise applications, with proved exploits confirmed against identity and developer systems including Keycloak, Jira, Confluence, and Jenkins.
- AI-driven discovery: The exposure follows a parallel discovery in PHP by Calif researchers, spotlighting how machine-assisted auditing tools are rapidly shrinking the window between bug detection and weaponization.
- Global response: Oracle rolled out fixes within a monthly update spanning 652 issues, prompting coordinated patching advisories from CISA, alongside authorities in the UK, Germany, and South Korea.
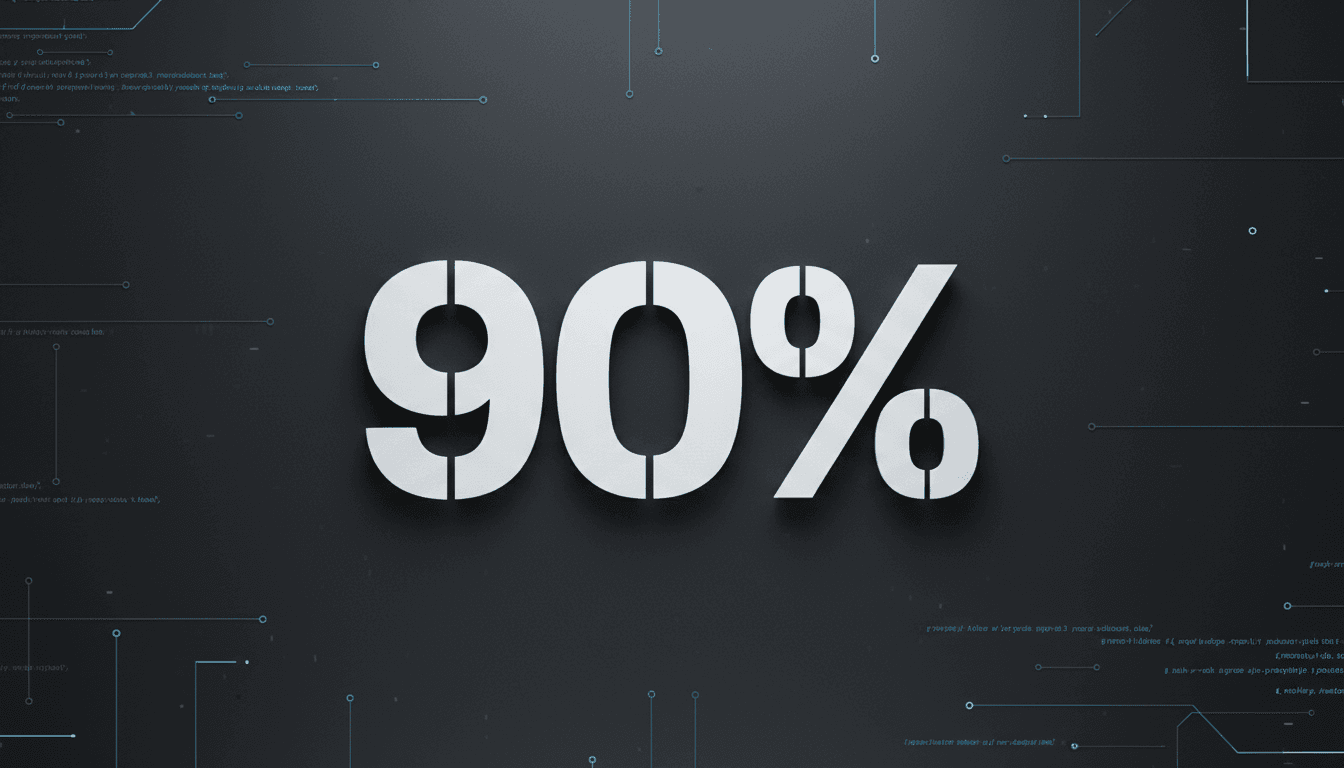
The Number
— The share of Fortune 500 corporations that rely on Java for back-end enterprise architecture, demonstrating the baseline surface area open to this vulnerability.
Takeaway
Enterprise security teams will increasingly pivot toward AI-assisted vulnerability management to audit third-party code stacks before automated scanners locate exploitable memory flaws first.
Latest tech news, product reviews, and analysis for consumers and professionals.
"CNET delivers accessible and detailed technology reporting, including trusted product reviews and how-to guides."
— A47 Editor
Critical Java Flaw Leaves Systems Open to Hackers
CNET reports a critical Java flaw that could allow hackers to take over systems without a password, leaving affected environments exposed to unauthorized access. The base report frames the bug as a serious threat to systems running the widely used Ja...
Consumer technology news with AI coverage.
"Gadget and tech site reporting on AI in products."
— A47 Editor
AI found a hole in Java, and it starts with 'AAAAAAAA...'
A newly discovered security flaw in Java, reported by Engadget, reportedly allows hackers to take over systems, and the article notes the bug was found with the help of AI and begins with a string of repeated 'A' characters. The vulnerability is said...
Covers consumer technology, electronics, gadgets, and product reviews.
"Engadget is a trusted source for gadget reviews and consumer tech news, known for its hands-on analysis and industry coverage."
— A47 Editor
AI found a hole in Java, and it starts with 'AAAAAAAA...'
A newly discovered security flaw in Java, reported by Engadget, reportedly allows hackers to take over systems, and the article notes the bug was found with the help of AI and begins with a string of repeated 'A' characters. The vulnerability is said...
Consumer tech news, reviews, and buying guides for gadgets and electronics.
"TechRadar is known for comprehensive buying advice, hardware reviews, and consumer tech news targeted at mainstream audiences."
— A47 Editor
Java hit by major security flaw — here's what we know about Java4Shell so far
Java has been hit by a major security flaw known as Java4Shell, which enables data exfiltration and remote code execution and can be exploited through a surprisingly simple method, according to TechRadar's coverage of the vulnerability.
Corporate news, economic trends, and markets with UK and global scope.
"BBC News is widely regarded as reputable and impartial, with a public service mandate."
— A47 Editor
Security flaw found in Java, world's third-largest programming language
A security flaw has been identified in Java, the third-largest programming language in the world, after a technology start-up that had previously found a flaw in PHP used artificial intelligence to uncover a critical software bug in the language, as ...